> ## Documentation Index
> Fetch the complete documentation index at: https://developers.argosidentity.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Encryption & Decryption Tool
> A desktop tool for encrypting and decrypting query strings and API data, and for receiving webhooks on your own machine. Covers installation, each tab, and common problems.
## What this tool is for
Use it during integration work to answer questions like "is my ciphertext correct?" and
"what does a webhook actually look like?" You can try values and see results before writing any code.
Pick the parameters for a LiveForm URL and get the `encrypted=` value
Build Face Auth URLs and their ciphertext
Call all 17 endpoints from a form and copy the cURL
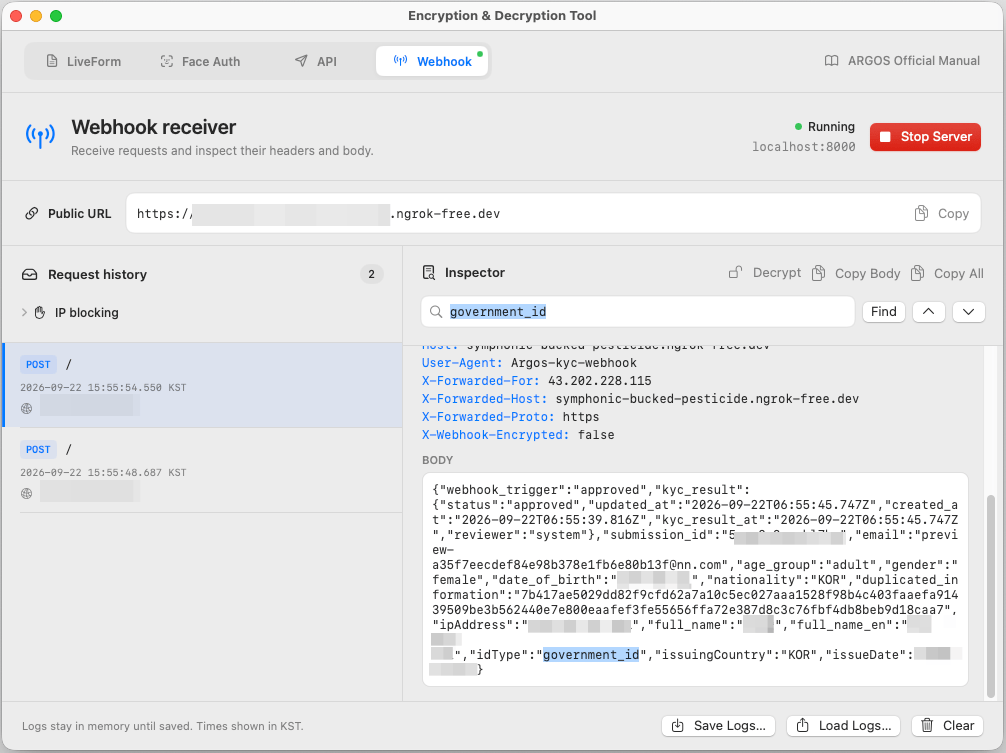
Receive webhooks on your machine, inspect them, and decrypt the body
This tool is for development and testing. Values live in memory only and are never saved,
and API keys are masked on screen. It is not meant to be part of your production flow.
## Download
Requires macOS 13 (Ventura) or newer.
[Download for macOS](https://argos-logo.s3.ap-northeast-2.amazonaws.com/developer_guide/EnDecryptGUI_Mac_0922.zip)
You get `EnDecryptGUI.app`. Moving it to your Applications folder is convenient.
Double-clicking shows an "unidentified developer" warning.
Open **System Settings → Privacy & Security**, scroll down, and next to
`"EnDecryptGUI" was blocked` click **Open Anyway**.
You only need to do this once.
Requires 64-bit Windows 10 or newer. The .NET runtime is bundled, so nothing else to install.
[Download for Windows](https://argos-logo.s3.ap-northeast-2.amazonaws.com/developer_guide/EnDecryptGUI_Win_0922.zip)
**Extract the whole folder.** Copying only `EnDecryptGUI.exe` will not work —
it needs the DLLs sitting next to it.
If "Windows protected your PC" appears, click **More info**, then **Run anyway**.
This notice appears because the app is not code-signed.
## Switching tabs with the keyboard
You can also switch tabs from the keyboard: `⌘1`-`⌘4` on macOS, `Ctrl+1`-`Ctrl+4` on Windows,
in the order LiveForm, Face Auth, API, Webhook. Hover a tab to see its shortcut.
 ## Before you start — two things to check
Dashboard → **Project Management → Project Settings → Integration Info**.
Every encryption and decryption in this tool is based on that key.
Dashboard → **Project Management → Security Settings → Data Protection** shows
whether your project uses `ECB` or `GCM`.
If the tool's **Encryption** selector does not match, results will not line up.
The tool defaults to `ECB` and resets to `ECB` every time you relaunch it.
The **Encryption: ECB / GCM / CBC(Webhook)** selector at the top chooses *how* to encrypt.
It is not the Encrypt/Decrypt radio buttons, which choose *which direction* to convert.
| Option | When to use it |
| ---------------- | -------------------------------------------------------- |
| **ECB** | Your dashboard is set to ECB. Query strings and API data |
| **GCM** | Your dashboard is set to GCM. Query strings and API data |
| **CBC(Webhook)** | Opening the `data` value you received in a webhook |
## LiveForm tab — building URL parameters
This is where you produce the `encrypted=` value for a LiveForm URL.
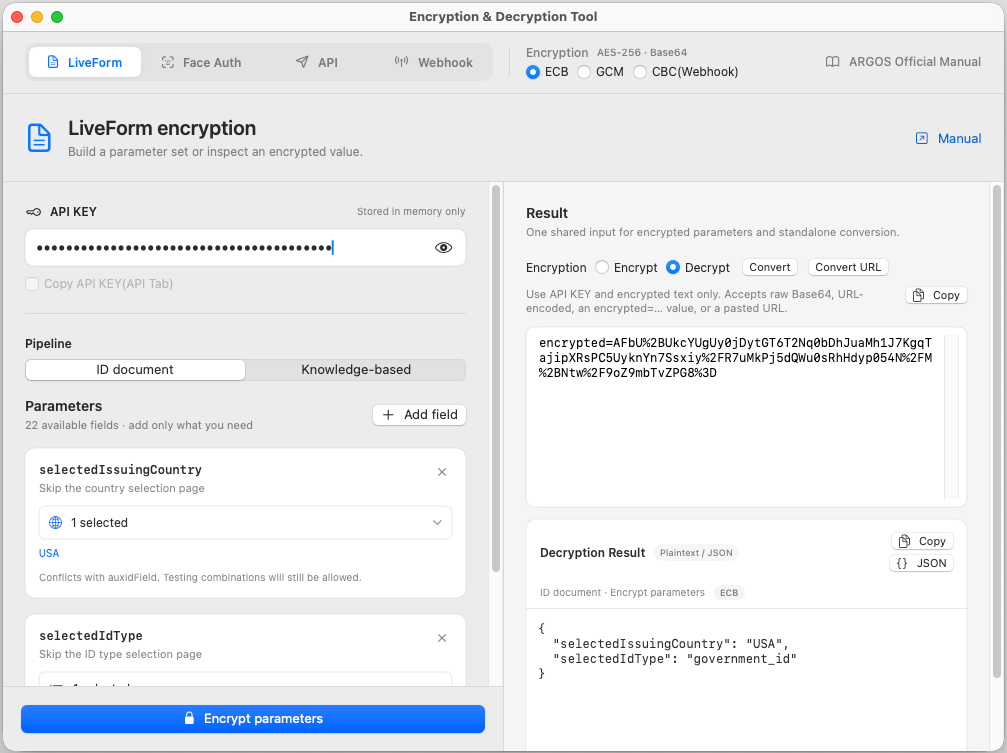 Pick **ID document** or **Knowledge-based**. Each keeps its own draft, so switching
back and forth never loses what you typed.
The eye button toggles visibility.
Pick parameters one at a time and fill in values. Multi-select items such as countries
and document types are joined with commas in the order you selected them.
The input box on the right is filled with `encrypted=` followed by the URL-encoded ciphertext.
**Copy it and append it to your URL.**
**Decryption Result** below shows the original JSON you just encrypted, formatted for reading,
so you can confirm what went in.
**Warnings do not block encryption.** For example, `selectedIdType` without
`selectedIssuingCountry` shows a notice but still encrypts. That is deliberate, so you can
test invalid combinations.
Only three things actually block encryption — no parameters at all, an empty API key,
or a malformed color or date.
### The `knowledgePrefill` editor
In the Knowledge-based pipeline, `knowledgePrefill` opens its own editor.
Choose from `name`, `gender`, `birthDate`, `nationality`, `SSN`, `address`, and `phoneNumber`,
type the values, and the combined string such as `gender=male,birthDate=1990-01-01`
is composed live.
To try keys that are not in the list, switch to **Raw text** mode.
The Fields and Raw drafts are kept separately.
Fields you leave empty are omitted. Greyed-out hints such as `Jane Doe` are examples,
not defaults — only what you actually type gets encrypted.
## The converter on the right — one value, quickly
Use this to encrypt or decrypt **any text** without building a parameter set.
You only need the API key and the input box. It is available on both the LiveForm and Face Auth tabs.
| Button | Result |
| ---------------------------------- | --------------------------------------------------------------------- |
| **Convert** (Encrypt selected) | Raw ciphertext — Base64 for ECB/CBC, hex for GCM |
| **Convert URL** (Encrypt selected) | Ciphertext, already URL-encoded. Paste it straight after `encrypted=` |
| **Convert** (Decrypt selected) | The original plaintext |
When decrypting, all four of these are accepted as-is:
* raw ciphertext
* URL-encoded ciphertext
* `encrypted=...`
* a full URL containing an `encrypted` parameter
**GCM produces a different result every time, even for the same input.** That is expected —
it mixes in fresh randomness for security. Decrypting always returns the same original value.
## Face Auth tab
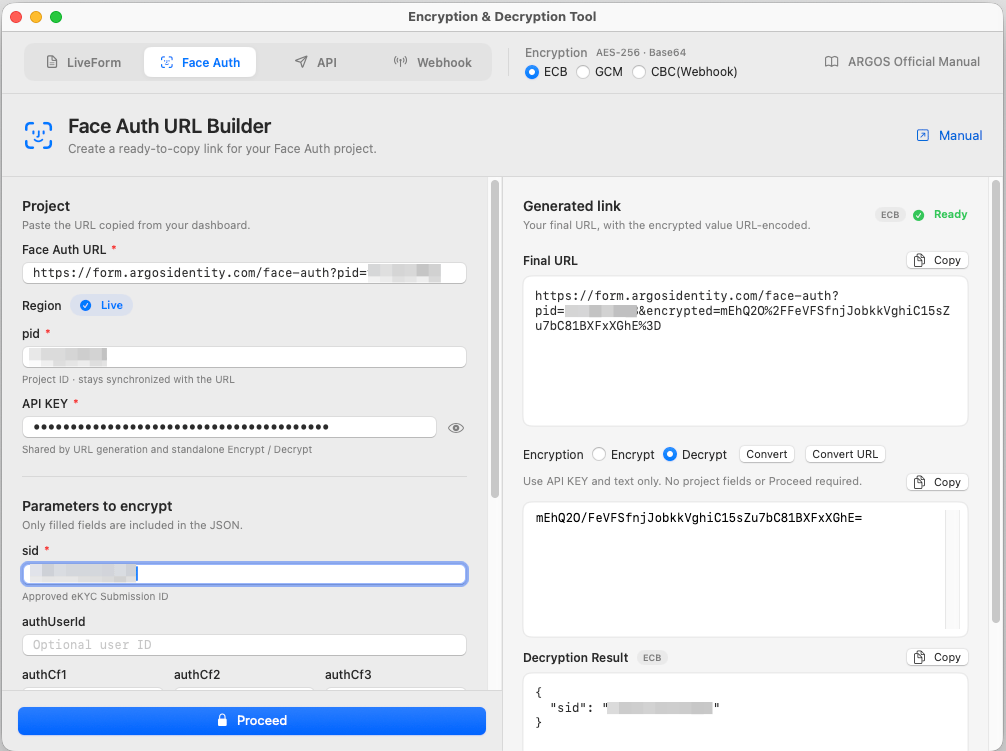
Paste the Face Auth URL from the dashboard and the region is detected automatically and `pid` is filled in.
Enter the API key and an **approved** `sid`, then click **Proceed** to build the final URL.
 | Region | Base URL |
| ------------ | ------------------------------------------------- |
| Develop (US) | `https://form-dev.argosidentity.net/face-auth` |
| Develop (KR) | `https://form-dev-kr.argosidentity.net/face-auth` |
| Live | `https://form.argosidentity.com/face-auth` |
`pid` and `lang` are not encrypted. What gets encrypted is `sid` plus the optional fields you filled in.
`mainColor` and `innerColor` are currently disabled — visible but not editable, and left out of the result.
## API tab
Fill in a form for any of the 17 endpoints and send a real request.
Set the base URL and API key on the left, fill parameters on the right, then click **Proceed**.
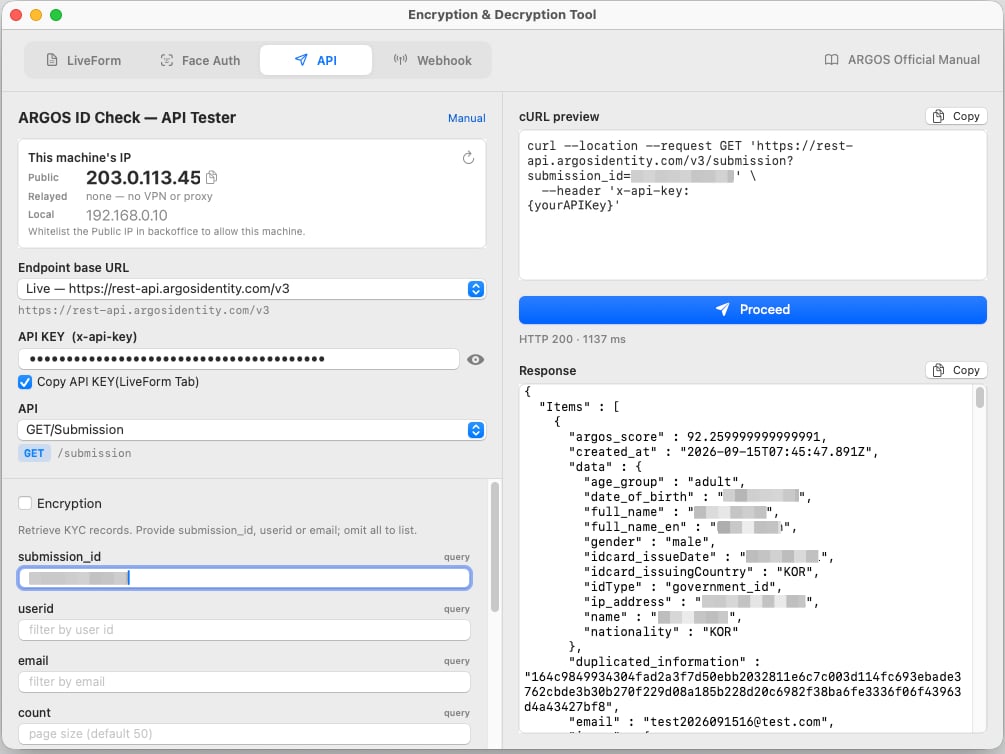 * The **cURL preview** updates as you type. Copy it and run it in a terminal as-is.
* Responses show the HTTP status and elapsed time. JSON is formatted for reading.
* Your public IP, local IP, and VPN status are shown too, which helps with IP-restricted projects.
**These are real requests.** Read operations are safe, but create, update, and delete endpoints
take effect for real. Do not test against a production project — create a separate test project.
### Using Secure Data Transfer (encryption)
If **Secure Data Transfer** is enabled on your project, Submission endpoints show an
**Encryption** checkbox. Ticking it replaces the normal inputs with a single
`data (encryption)` field.
```json theme={null}
{ "submission_id": "abc123def456" }
```
Use the converter on the LiveForm or Face Auth tab with **ECB**.
Both raw and URL-encoded ciphertext are accepted.
The response comes back encrypted too, as `{"data":"...","isEncrypted":true}`.
Copy the `data` value and run it through the converter in **Decrypt** mode.
How the ciphertext travels differs per method. See
[Secure Data Transfer Options](/en/idcheck/getting-started/encrypt-and-decrypt-data/overview#4-secure-data-transfer-options)
for the exact contract.
## Webhook tab — receiving webhooks on your machine
A webhook is ARGOS sending results **to your server**. But the machine you develop on has no
public address, so ARGOS cannot reach it.
**ngrok** solves this. It creates a temporary public address and forwards anything sent there
to your machine.
```
ARGOS server → https://xxxx.ngrok-free.app → your PC (localhost:8000) → this tool
```
**This tool uses port 8000 on your machine.** That cannot be changed.
If you follow the steps below, the tool runs `ngrok http 8000` for you —
you never have to type the command yourself.
 ### Step 1 — Install ngrok
Open Terminal and install with Homebrew.
```bash theme={null}
brew install ngrok
```
**Install it with Homebrew.** The tool only looks in these three locations:
* `/opt/homebrew/bin/ngrok`
* `/usr/local/bin/ngrok`
* `/opt/homebrew/opt/ngrok/bin/ngrok`
A binary downloaded from the website into Downloads or the Desktop will not be found.
If you already did that, move it to `/usr/local/bin/`.
Open PowerShell and install.
```powershell theme={null}
winget install ngrok.ngrok
```
**Close and reopen PowerShell** afterwards so it is picked up.
On Windows the tool searches in this order:
`tools\ngrok.exe` inside the app folder → the app folder → the WinGet links folder → your PATH.
A winget install is found automatically.
### Step 2 — Connect your ngrok account (once)
ngrok requires a free account.
Sign up at [ngrok.com](https://ngrok.com) and copy the token from the
**Your Authtoken** page.
```bash theme={null}
ngrok config add-authtoken YOUR_TOKEN
```
`Authtoken saved` means you are done. This is once per computer.
### Step 3 — Start the server
The tool opens port 8000 and launches ngrok for you. It takes a few seconds.
An address starting with `https://` appears. Click **Copy** next to it.
The status reads **Running** and a green dot appears on the Webhook tab.
Paste it into **Project Management → Webhook Settings** and save.
Run one KYC submission. The request appears in the list on the left immediately.
Click it to see the timestamp, sender IP, headers, and body on the right.
**On a free ngrok account the address changes every time you restart it.**
When it changes, update the webhook setting in the dashboard again.
### Decrypting what you received
If Secure Data Transfer is enabled, the body arrives as ciphertext.
Click **Decrypt** above the body to open it.
On success a **Decrypted** badge appears and the body is replaced with readable JSON.
Decrypt uses **the API key you entered on the LiveForm tab**.
Enter it there first, or you will get a notice saying the key is missing.
It also always uses **CBC**, regardless of the Encryption selector at the top,
because webhook bodies are specified to use CBC. You do not need to change the selector.
**Save Logs…** always exports the **originally received** bodies.
Neither the decrypted view nor your API key is written to the file.
### Trying IP blocking
Expand **IP blocking** at the bottom left and enter an IPv4 address to answer requests from it
with 403. Those appear in the list as red **BLOCK** entries. Useful for checking retry behavior.
## Troubleshooting
Usually a **mismatched algorithm**. Check whether your dashboard
(**Security Settings → Data Protection**) says `ECB` or `GCM`, and set the tool's
Encryption selector to match.
The tool resets to `ECB` on every launch, so a GCM project needs it selected each time.
If the algorithm is right, check the API key. A stray leading or trailing space is a common
cause — the tool uses exactly what you typed, so one extra space changes everything.
Check whether you **URL-encoded it twice**. This is by far the most common cause.
The result of **Convert URL** is **already encoded**. Paste it straight after `encrypted=`.
Running `encodeURIComponent()` on it again in your code turns `%2B` into `%252B` and breaks it.
| Situation | Button to use |
| ---------------------------- | ---------------------------------------------- |
| Pasting directly into a URL | **Convert URL** |
| Encoding it yourself in code | **Convert** (take the raw value and encode it) |
Wrong encoding can come back **without an error, just with an empty result**.
If you see "no error but no results", suspect this first.
**ngrok not found** — check how you installed it. On macOS it must be in a Homebrew location;
on Windows you may need to restart the app after installing.
**No auth token** — make sure you ran `ngrok config add-authtoken`.
**`ERR_NGROK_334`** — ngrok is already running somewhere else under the same account.
A free account allows only one at a time. Stop the other one and try again.
**Port 8000 is in use** — another program is using it. Close that program and retry.
This means the tool found an ngrok that was already running and is reusing it. That is normal.
It only reuses one that forwards to **port 8000**. If you started
`ngrok http 3000` yourself, the tool ignores it.
If you want to start ngrok yourself, use exactly:
```bash theme={null}
ngrok http 8000
```
In that case **Stop Server** will not shut that ngrok down, because you started it.
1. Make sure you pasted the **current** public URL into the dashboard webhook settings.
A free ngrok account changes the address on every restart.
2. Make sure the address starts with `https://`.
3. Make sure you did not leave an address in IP blocking.
Check that you extracted the **entire folder**.
Moving `EnDecryptGUI.exe` on its own will not work — all the DLLs in the same folder are required.
## Notes
* Inputs, API keys, and conversion results live **in memory only**. They disappear when you quit and are never written to disk.
* The LiveForm and Face Auth tabs use no network at all. Everything is computed locally.
* Only the API and Webhook tabs use the network.
* Each tab's API key is independent. The one exception is Webhook's Decrypt, which reads the LiveForm key.
For algorithms, key derivation, and per-language sample code, see the Data Encryption and Decryption page.